
Company
Containing privilege is not a new problem. The actor is.
We spent our careers deciding what contractors, vendors and service accounts were allowed to do inside production estates. Then agents arrived — faster, more numerous, and granted privilege on purpose, because that is what makes them useful.
What we do
Enterprises are deploying AI agents faster than they can govern them. Those agents get real access to real systems — because that is what makes them useful — and today nobody can say what any of them is actually allowed to do once it is there.
Evren gives security teams one place to decide that.
Every action an agent takes on a machine is checked against your policy before it happens, and written to a record nobody can quietly edit. Your teams get agents that work. You get limits that hold, and evidence that stands up afterwards.
What our customers get
- Agents deployed in production without writing an exception
- A clear answer to which agent did what, on which machine, and when
- Proof that holds up in an audit or an incident review
- All of it working with the identity provider and SIEM you already run
Vision
Every enterprise will run more agents than employees. The organisations that pull ahead will be the ones that can say yes to them quickly — because they have real limits in place, not because they stopped asking the question.
We are building the layer that makes yes the safe answer.
How we work
Say the limits first
We publish what our product does not do before anyone asks. Security teams have heard enough vendors claim everything.
Claims should be enforced, not asserted
If we say it, something in our build fails when it stops being true. A document is true once; a test stays true.
The agent keeps working
Security that breaks the thing the business wanted gets switched off. A denied action is a denied action, not an outage.
Build for the operator
The person who gets paged at three in the morning is the person we design for.
Team
Two founders who were on the other side of this problem — running security for enterprises, deciding what thousands of people and systems were allowed to do.
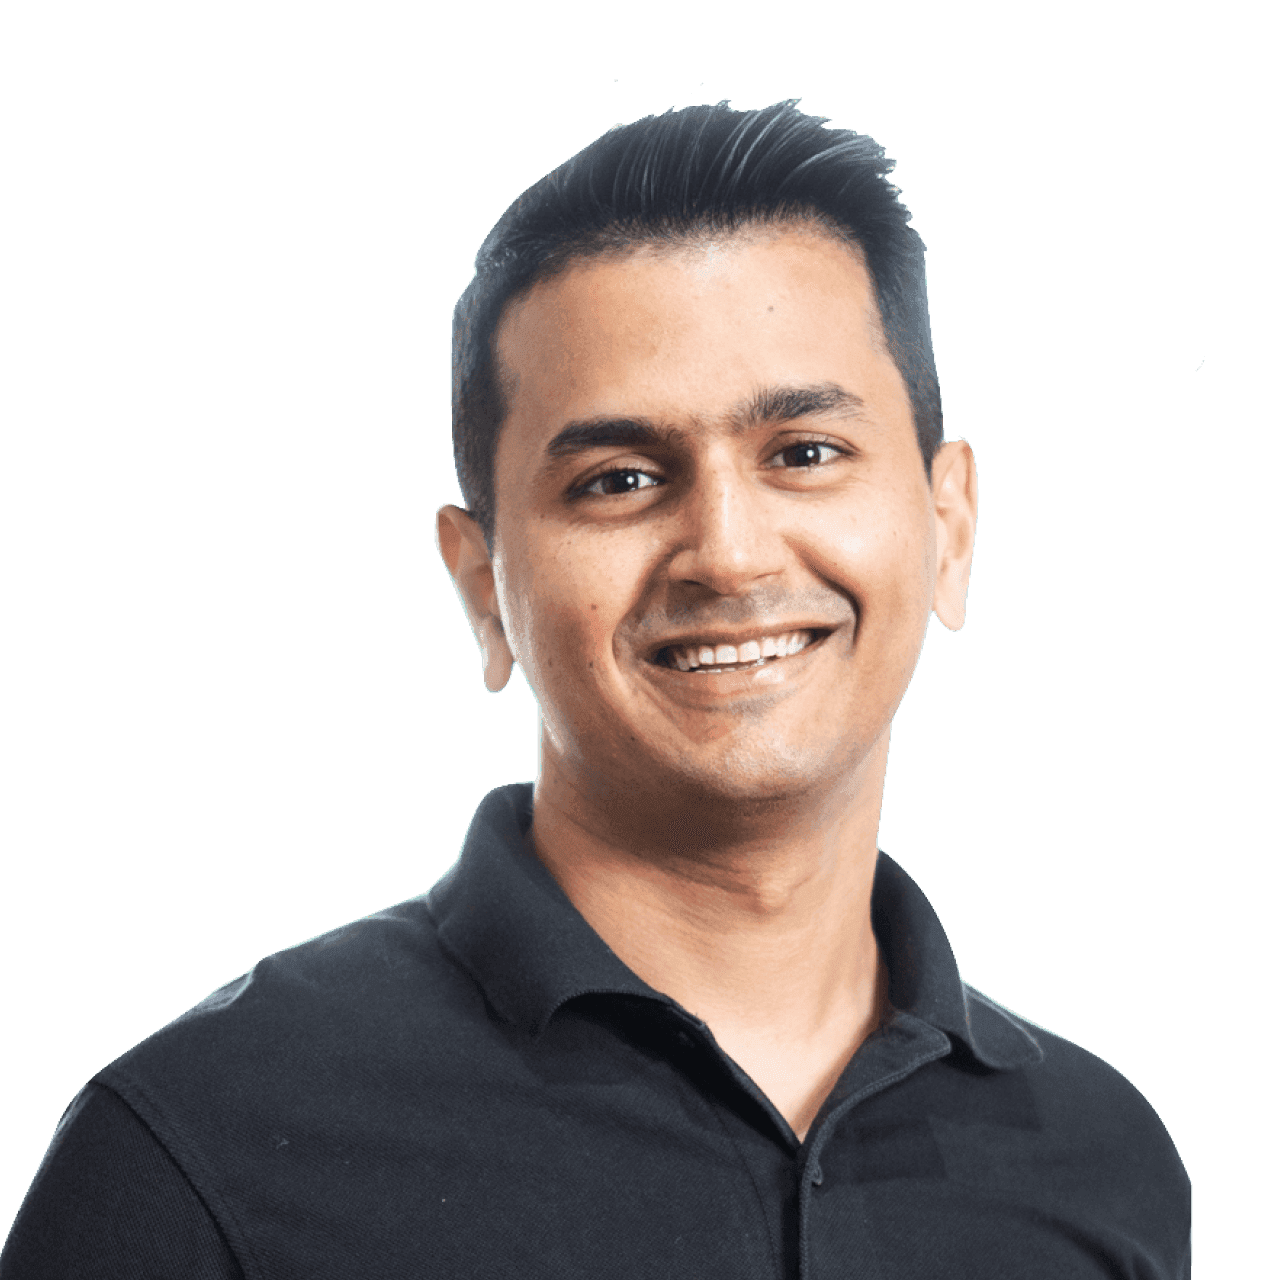
Gaurav Nagar
Co-founder & CEO
Product and customer focus
17 years securing enterprises across Southeast Asia. Head of Security at Lazada and AirAsia Group.
LinkedIn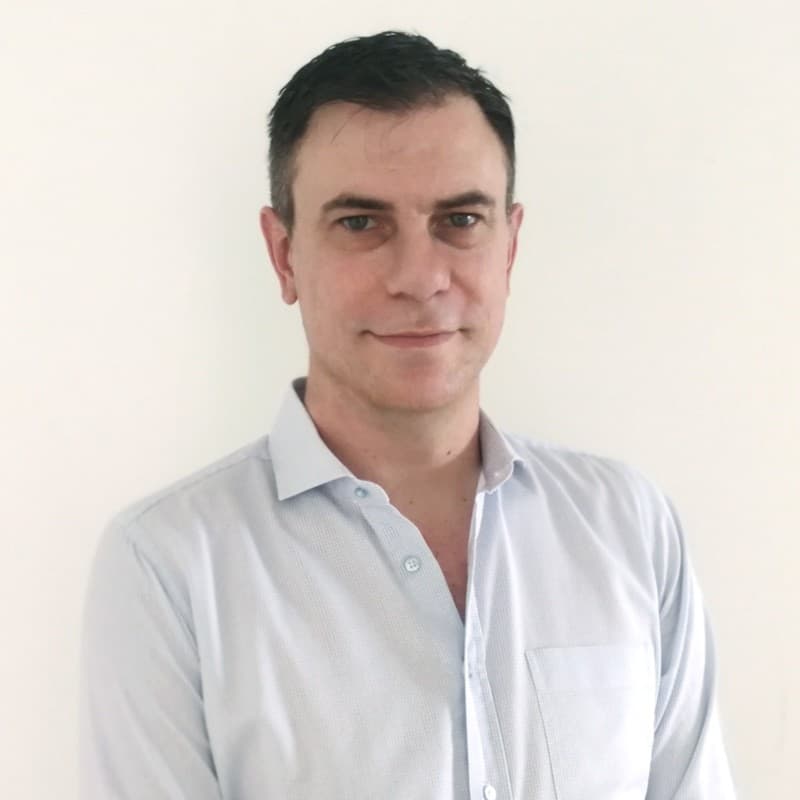
Fabrice A. Marie
Co-founder & CTO
CISO · Ethical hacker · Linux
25 years in security, kernel to boardroom. Former CISO at Lazada and AirAsia. Netfilter contributor.
LinkedInCareers
Small team, privileged code path, very little tolerance for hand-waving. If that sounds right, write to careers@evren.co.
Systems Engineer, Rust
Kernel-adjacent work: seccomp, Landlock, process lifecycle. You care about the privileged path and have opinions about fail-closed defaults.
Product Engineer, Console
Turn a stream of signed decisions into something a security team can act on. TypeScript, React, and a real tolerance for information density.
Not seeing your role? We read everything sent to careers@evren.co.
Talk to the people who built it
No SDR layer. Questions about the architecture, the threat model or a pilot go straight to a founder.